Joomla CAPTCHA in Joomla 5 and 6.2: Built-in Proof of Work, reCAPTCHA v3 and More (Tested)
Joomla 6.1+ has a built-in, key-free Proof of Work CAPTCHA; Joomla 5 needs a plugin. Setup steps, tested results, form coverage and fixes.
 Abhilash SahooFounder & CEO, Infyways
- Published
- Updated
- Reading time
- 6 min read
On this page 9 sections
- Does Joomla have a built-in CAPTCHA?
- Which CAPTCHA should I use for Joomla?
- How do I enable the Proof of Work CAPTCHA in Joomla 6.2?
- Does the Proof of Work CAPTCHA actually stop bots?
- Which Joomla forms use the CAPTCHA?
- How else can I stop Joomla form spam?
- Is the CAPTCHA GDPR-friendly and accessible?
- Troubleshooting
- FAQs
Updated 15 October 2026 · By Abhilash Sahoo, Founder, Infyways
Quick answer:
- Joomla 6.1 and later (including Joomla 6.2, the latest version) include a built-in CAPTCHA - Proof of Work plugin. It needs no API keys. Go to System → Global Configuration → Site → Default Captcha, choose it, and save.
- Joomla 5 has no CAPTCHA plugin in core. Install one from the JED that uses Joomla's Captcha API (reCAPTCHA v3, Turnstile, Friendly Captcha and others), enter its keys, and select it as the Default Captcha.
Either way, the CAPTCHA then protects registration, password reset, contact and front-end article forms. Login forms have no core CAPTCHA field.
I installed a fresh Joomla 6.2.0 site (PHP 8.4) and a Joomla 5.4.10 site to check every step below. I filled in the forms in Chrome and sent bot-style requests with curl. Images marked "real output" show what happened. Background: Joomla's announcement Built-in Captcha coming to Joomla core.
Does Joomla have a built-in CAPTCHA?
| Version | Core CAPTCHA | What I found |
|---|---|---|
| Joomla 4 | reCAPTCHA v2 and Invisible reCAPTCHA plugins | Need Google keys |
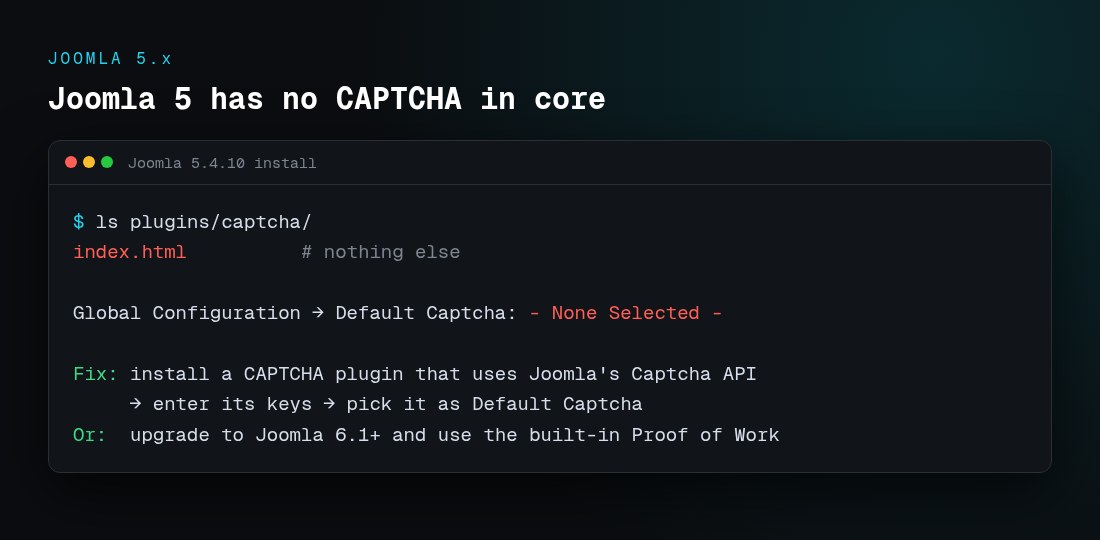
| Joomla 5.4.10 | None | plugins/captcha/ contains only index.html; Default Captcha shows "None Selected" |
| Joomla 6.1 / 6.2 | CAPTCHA - Proof of Work (ALTCHA library) | Enabled on a fresh install, but Default Captcha is still "None", so you must select it |
The reCAPTCHA plugins were removed during the Joomla 5 series. Joomla's team gave two reasons: they were outdated, and they depended on Google. On a site upgraded from Joomla 4, a leftover reCAPTCHA plugin can still appear in the list without working. Replace it rather than trust it.
Which CAPTCHA should I use for Joomla?
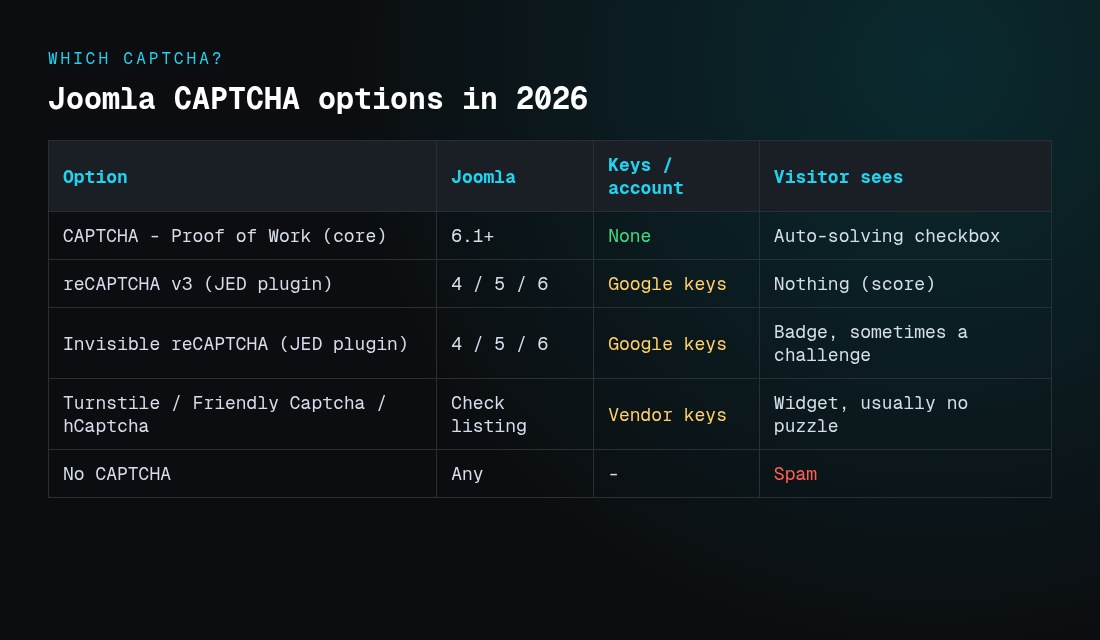
| Option | Joomla | Account / keys | Visitor experience | Good for |
|---|---|---|---|---|
| CAPTCHA - Proof of Work (core) | 6.1+ | None; no external service | Checkbox that solves itself | Most sites on Joomla 6; privacy-sensitive sites |
| reCAPTCHA v3 plugin (e.g. Sharky's, free on the JED) | 4 / 5 / 6 | Google keys | Invisible, score-based | Joomla 5 sites already using Google |
| Invisible reCAPTCHA plugin (e.g. Nicholas Dionysopoulos's) | 4 / 5 / 6 | Google keys | Badge, occasional challenge | Replacing Joomla 4's old core plugin |
| Turnstile, Friendly Captcha, hCaptcha plugins | Check each listing | Vendor keys | Widget, usually no puzzle | Sites that avoid Google |
Choose a plugin built on Joomla's Captcha API. It then appears in the Default Captcha list and works with every core form. Before you rely on Google: the invisible plugin's documentation says keys must now live in a Google Cloud project, with a limited free tier. Joomla's announcement says reCAPTCHA now asks for a payment method. Check Google's current terms.
How do I enable the Proof of Work CAPTCHA in Joomla 6.2?
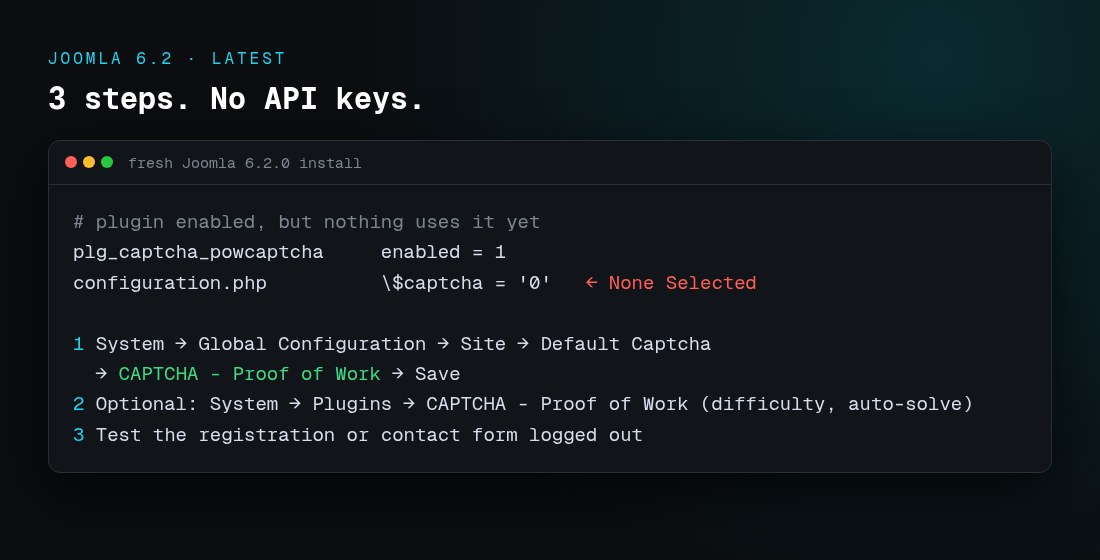
- Go to System → Global Configuration → Site → Default Captcha, choose CAPTCHA - Proof of Work, and save. On my fresh 6.2 install, the only options were "- None Selected -" and this plugin.
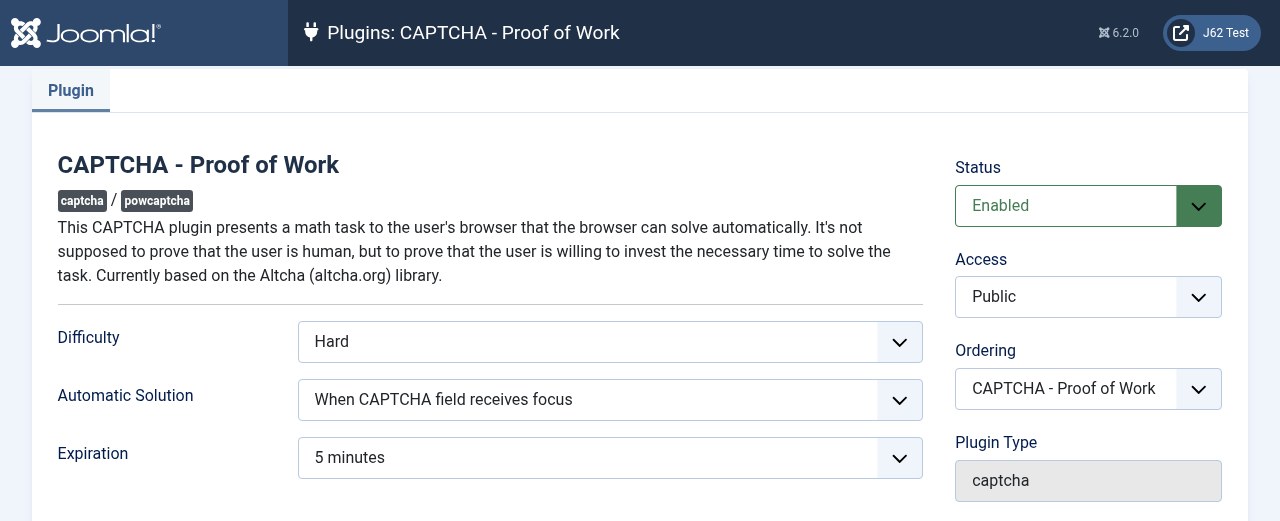
- Optionally, adjust it under System → Plugins → CAPTCHA - Proof of Work:
- Difficulty: Easy, Moderate (the default), Hard, or Custom with a Maximum Number.
- Automatic Solution: off, when the field gets focus (the default), on page load, or on submit.
- Expiration: 1 minute, 5 minutes (the default), 10 minutes or 1 hour.
- Log out and test the registration or contact form.
Does the Proof of Work CAPTCHA actually stop bots?
It doesn't try to prove the visitor is human. The browser has to spend computing time on a hashing task (SHA-512 in the 6.2 source) before the form is accepted. That cost adds up for spam sent in bulk. Here's what I measured:
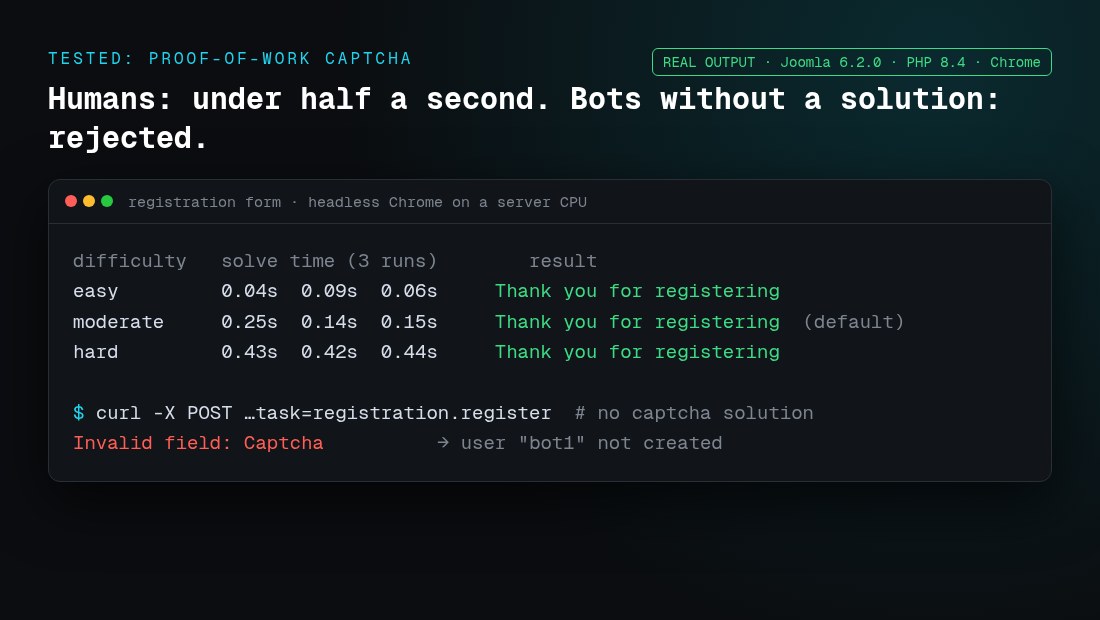
- Real browser: solved in 0.04–0.09 s on Easy, 0.14–0.25 s on Moderate and about 0.43 s on Hard (3 runs each, headless Chrome on a server CPU). Each registration went through. Phones will be slower.
- Bot without a solution: a direct POST to
task=registration.registerreturned "Invalid field: Captcha", and no user was created. - Replays: each challenge key is stored in the session and cleared once it's used, so a solution can't be reused (from the 6.2 source).
To be honest about the limits: a determined bot running a real browser can solve the task too, just more slowly. Joomla's announcement mentions plans to raise the difficulty for repeat requests from the same IP address. The 6.2.0 source doesn't include that yet. For heavy spam, combine it with the steps in the next section.
Which Joomla forms use the CAPTCHA?
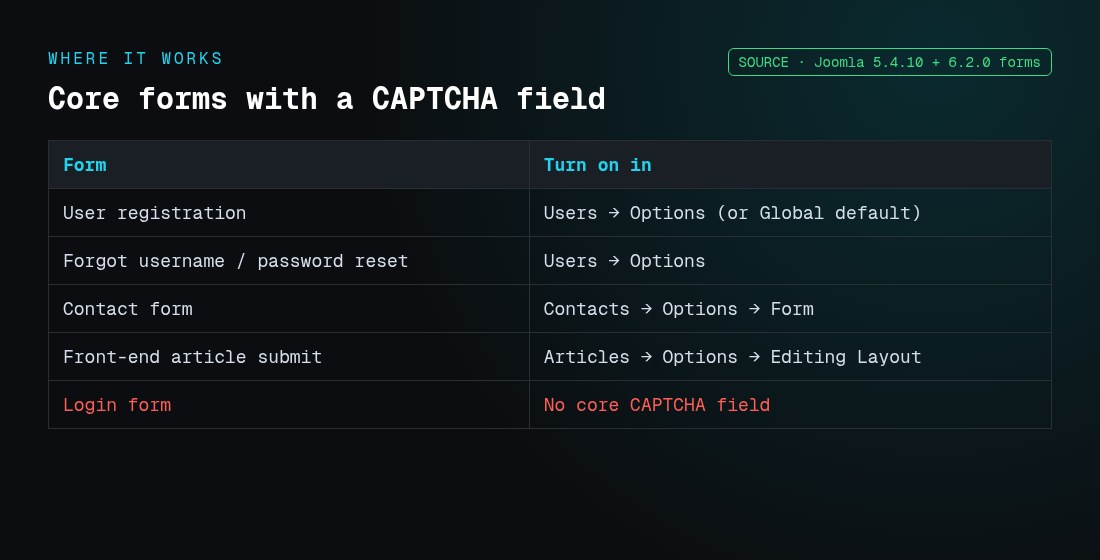
| Form | Where to turn it on |
|---|---|
| User registration, forgot username, password reset | Users → Options → User Options → Captcha (or leave "Use Default") |
| Contact form | Contacts → Options → Form tab → Allow Captcha on Contact |
| Front-end article submission | Articles → Options → Editing Layout → Allow Captcha on submit |
| Login | No core CAPTCHA field. Use strong passwords, MFA and rate limiting instead |
| Third-party forms (RSForm, Convert Forms and so on) | That extension's own settings, if it supports Joomla's Captcha API |
I checked this list against the type="captcha" fields in the Joomla 5.4.10 and 6.2.0 form files. Both versions have the same five forms.
How else can I stop Joomla form spam?
- Turn off what you don't use. If visitors don't need accounts, set Allow User Registration to No (Users → Options).
- Require activation (Self or Administrator) so bot accounts never become active.
- Block repeat offenders at the server with
.htaccessor your firewall (see our Joomla .htaccess guide). - Keep Joomla and form extensions updated. Spam often arrives through an old form extension. See the Joomla security guide.
Is the CAPTCHA GDPR-friendly and accessible?
The core Proof of Work plugin runs entirely on your server and the visitor's browser. There are no API keys and no external service. Joomla's announcement highlights this, and it also calls the method accessible, because there's no image or audio puzzle. With Google or other hosted CAPTCHAs, the visitor's browser contacts the vendor, so your cookie and privacy notices may need to mention it. See disabling cookies for visitors and our European Accessibility Act guide.
Troubleshooting
| Symptom | Cause | Fix |
|---|---|---|
| Default Captcha only shows "None Selected" | No CAPTCHA plugin installed or enabled | Joomla 6: enable CAPTCHA - Proof of Work. Joomla 5: install a plugin |
| CAPTCHA enabled but not on the form | Component set to "None", or the form isn't a core form | Check each component's Options; check the third-party form's settings |
| Widget area is blank | The plugin's JS didn't load (blocked by CSP, wrong live_site, or a JS optimiser) | Check the browser console; exclude the CAPTCHA script from minify/defer tools |
| "Invalid field: Captcha" for real users | Solution expired, or the session was lost (cache, cookies) | Raise Expiration; exclude form pages from page caching |
| Old reCAPTCHA plugin listed but broken after an upgrade | Leftover Joomla 4 plugin | Install a maintained plugin, select it, and disable the old one |
| reCAPTCHA "Invalid domain for site key" | Domain missing in Google's console | Add the domain, including staging |
| Spam still arrives | The spam comes through a form without a CAPTCHA, or from human spammers | Find which form it comes from; add moderation, activation or rate limits |
| Form slow on phones | Difficulty set too high | Go back to Moderate or Easy |
FAQs
No. Joomla 5.4.10 ships no CAPTCHA plugin. Install a plugin that uses Joomla's Captcha API, or upgrade to Joomla 6.1 or later.
The plugin is enabled on a fresh install, but the Default Captcha is "None". You have to select it in Global Configuration.
No. The Proof of Work plugin uses the ALTCHA library and runs without any external service.
Yes, with a third-party plugin and Google keys. Check Google's current pricing and project requirements first.
Start with Moderate, the default. It took about 0.15 s in my tests. Use Hard only if spam keeps getting through, and test on a phone.
Joomla's core login form has no CAPTCHA field. Protect logins with strong passwords, multi-factor authentication and server-level rate limiting.
Yes. Each component's Options can override the global Default Captcha.
It can. The challenge is tied to the visitor's session, so a cached copy of the page may serve an old challenge. Exclude registration and contact pages from page caching.
It stops most bulk bots. Combine it with account activation, turning off unused forms and keeping your extensions updated.
Yes. We set up CAPTCHAs and clean up spam as part of Joomla support and maintenance, and we move Joomla 5 sites to 6 with our Joomla upgrade service. Read more about Joomla 6.
Filed under Joomla